Choosing tax providers is a decision about financial governance, not just tax return preparation. We assess two connected risks: whether sensitive information is handled appropriately and whether the resulting tax position can withstand Australian Taxation Office (ATO) scrutiny. Strong cybersecurity cannot rescue an unsupported deduction. Accurate calculations cannot compensate for exposed identity documents or compromised account access.
For business owners, directors and high-net-worth individuals, we recommend examining the complete process, from authorising an adviser and sharing records to approving a lodgement and responding to an incident. The objective is defensible reporting supported by controlled, traceable information.
Start with registration, authority and scope
We recommend confirming the registration of anyone providing tax agent services for a fee through the Tax Practitioners Board public register. An accounting qualification, software subscription or polished website does not replace the registration required for regulated services.
Registration is only the starting point. We also look for an engagement agreement identifying the relevant entities, services, responsibilities and exclusions. A company, discretionary trust, investment portfolio and SMSF can involve different obligations. An unclear engagement can leave a director assuming that someone is monitoring a deadline when nobody has accepted that responsibility.
When comparing tax providers, we distinguish authority to act from access to personal credentials. Where ATO client-to-agent linking applies, we recommend completing the authorisation through official ATO services. We do not recommend sharing a personal myGov password to establish an adviser relationship.
We also establish who can approve disclosures, instructions and lodgements. For family groups and companies with several directors, this prevents informal instructions from becoming unauthorised decisions. Clear authority protects confidentiality and creates accountability before financial information begins moving between systems.
How tax providers protect sensitive information
Limit access to the people who need it
We recommend assessing access controls at the individual user level. Shared accounts make it harder to establish who downloaded a document, changed bank details or approved a transaction.
Controls worth examining include multi-factor authentication, role-based permissions and prompt removal of access when staff or contractors leave. We also recommend checking whether the same controls extend to email, document storage and connected accounting applications, rather than only the main ledger.
For high-net-worth clients, separating entity access can be particularly valuable. A payroll administrator may need employee information without needing access to personal investment records or estate documents.
We expect tax providers to explain how access is granted, reviewed and withdrawn. A statement that a platform is “secure” is less useful than a clear description of permissions, monitoring and responsibility.
Protect documents throughout their lifecycle
We recommend an agreed document exchange method rather than ad hoc attachments containing TFNs, identity documents and bank statements. Secure portals can reduce exposure, but their effectiveness still depends on configuration, authentication and how users handle downloaded files.
Encryption during transmission and storage, device protection and recoverable backups address different risks. None replaces the others. We also recommend independently verifying requests to change bank details using a known contact number, not the number supplied in a suspicious message.
Retention deserves equal attention. We follow the applicable tax and corporate recordkeeping requirements rather than keeping everything indefinitely. Many business tax records generally need to be retained for five years, but exceptions apply. Company financial records generally require seven years, while asset records may need to remain available much longer.
Examine cloud services, outsourcing and AI
We recommend asking where information is processed, which service providers receive it and what contractual restrictions apply. Australian data hosting alone does not establish that a system is secure or that every confidentiality obligation has been satisfied.
Before tax providers introduce AI tools or external processing, we expect them to assess permitted disclosures, applicable privacy obligations and client permissions. The TPB confidentiality obligation generally prevents disclosure of information relating to a client's affairs to a third party without permission unless there is a legal duty to disclose.
For AI services, we examine whether client data can be retained, reused for model training or accessed by other parties. We recommend against entering identifiable client information into an unapproved public AI tool. Efficiency should come from controlled workflows, not from accepting unclear data-use terms.
Protect the evidence behind your ATO position
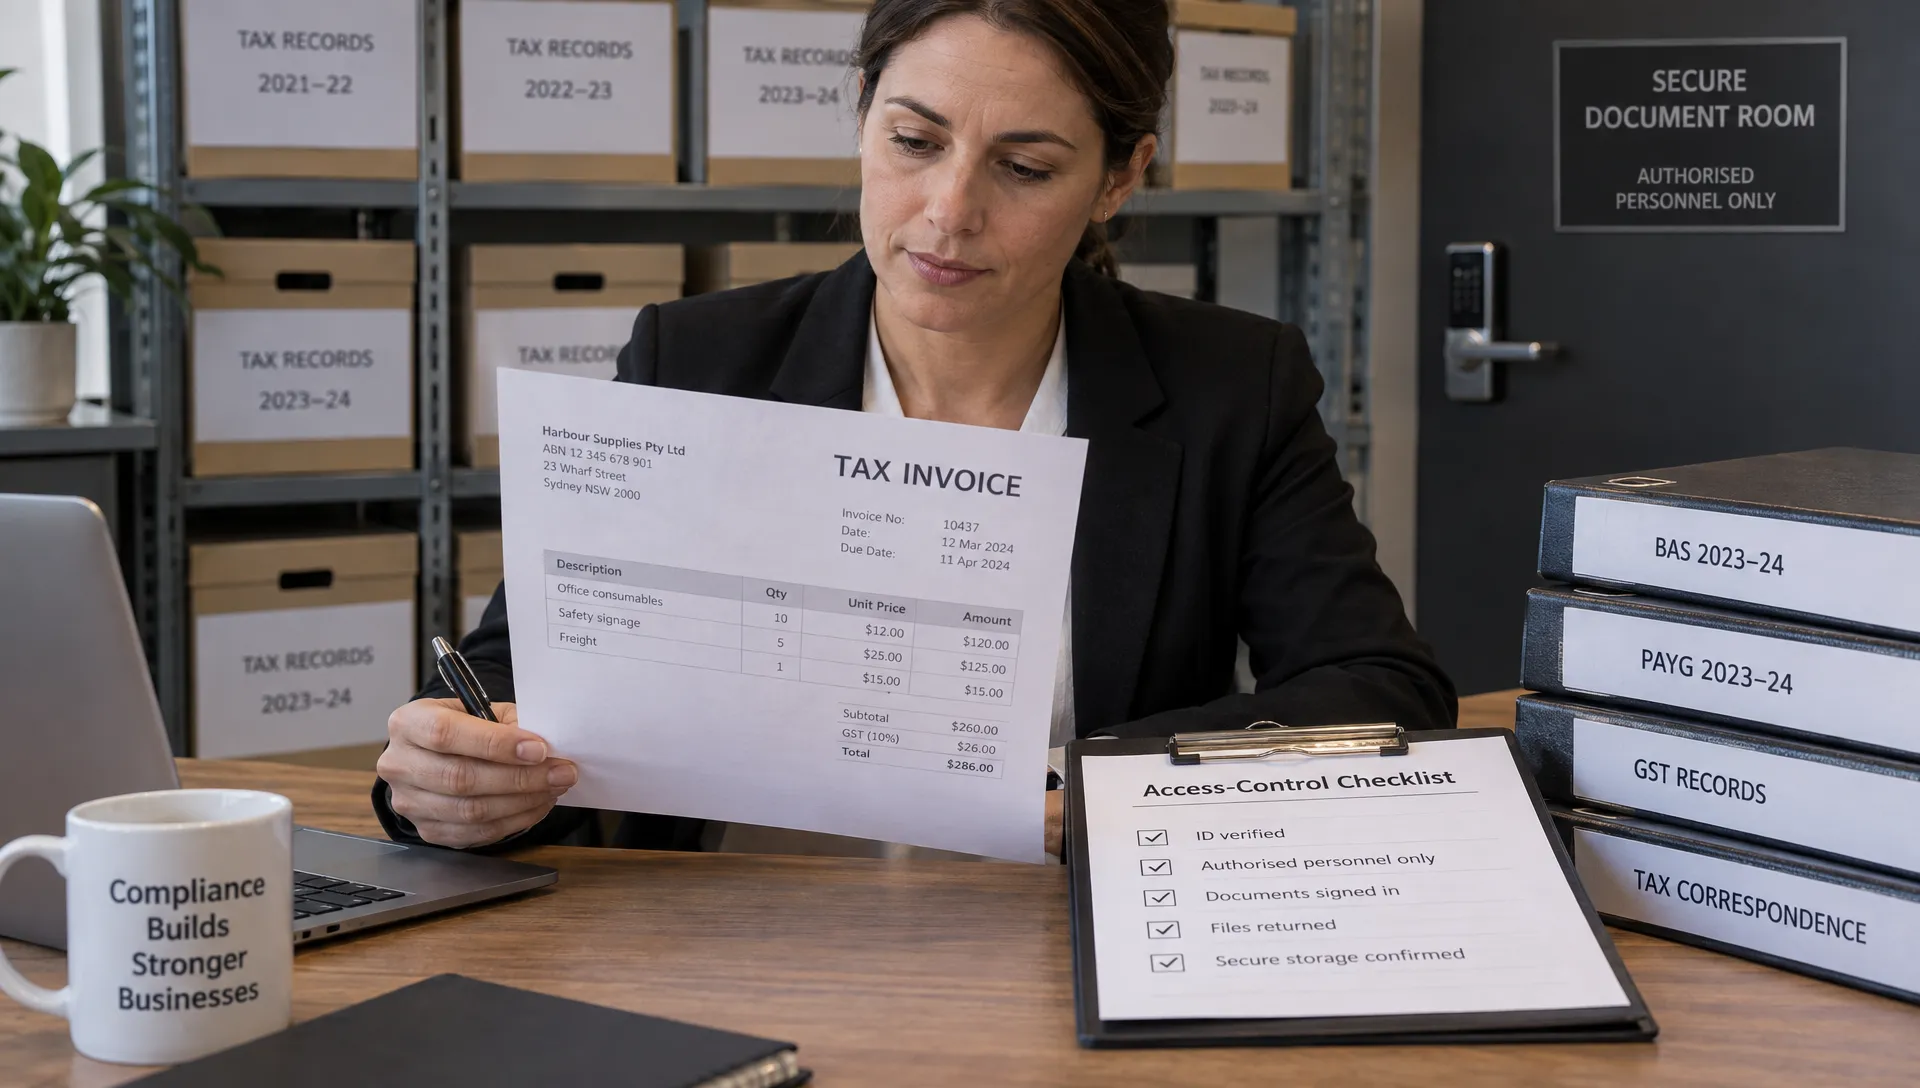
We treat an ATO position as the combination of reported figures, supporting records and the reasoning behind their tax treatment. An invoice proves that a supplier billed an amount. It does not, by itself, prove deductibility, entitlement to a GST credit or the correct year of recognition.
We therefore look beyond document collection. Income tax returns should be reconciled with the ledger and relevant BAS reporting, with legitimate differences explained. Payroll records should align with reporting and payment obligations. Significant deductions, related-party transactions and unusual adjustments need documented review.
The following controls help turn records into a defensible position:
| Area | Control we recommend | Evidence it preserves |
|---|---|---|
| Income and BAS | Reconcile reported amounts and explain differences | A bridge between the ledger and lodgements |
| GST credits | Check eligibility, tax invoices and private-use adjustments | Support for the credit claimed |
| Payroll and Superannuation | Reconcile payroll reporting, liabilities and payments | A record of obligations and their treatment |
| FBT | Review relevant benefits and supporting calculations | The basis for reporting or an exemption |
| Significant deductions | Record the facts and technical reasoning | Support for classification and timing |
| Lodgement approval | Retain the final version and client authorisation | Evidence of what was approved and submitted |
We expect tax providers to maintain this evidence alongside the numbers, rather than reconstructing the explanation after an ATO query arrives. Our discussion of company tax return errors that attract ATO attention explains why reconciliation gaps deserve attention before lodgement.
Example: commercial property painting expenditure
We can illustrate the distinction using property expenditure. If a commercial landlord engages a residential and commercial painting contractor in Melbourne, the quote, invoice and payment record help establish the work performed and its cost.
We still need to assess the property's circumstances. Painting that maintains an existing income-producing property may have a different treatment from work addressing deterioration present when the property was acquired, or work forming part of a broader improvement. Initial repairs and capital expenditure should not automatically be treated as immediately deductible repairs.
We recommend retaining the scope of work, relevant photographs, acquisition details and an explanation of the treatment adopted. Where GST is involved, we separately assess credit entitlement rather than assuming that every property-related invoice supports a credit.
This example also shows why confidentiality and substantiation belong together. We need sufficient evidence to support the claim, but we should not circulate unrelated tenant information or identity records with a contractor's invoice.
Use automation to identify exceptions, not replace judgement
Our AI-driven approach to accounting focuses on reducing repetitive processing and improving the usefulness of financial information. Automated capture, transaction matching and exception detection can support faster processing, greater accuracy and more current financial visibility when properly configured and reviewed.
We expect tax providers to explain where automation ends and professional judgement begins. A system may suggest a GST code or flag an unusual payment, but it cannot make every decision about business purpose, private use, capital treatment or the interaction between entities.
We recommend testing automated rules before relying on them, retaining original records and documenting material overrides. Changes to bank details, unusual journals and transactions outside established patterns warrant additional review. An incorrect rule can repeat the same error across hundreds of transactions.
We use accurate bookkeeping and compliance as foundations for strategic advisory and corporate growth. Reliable information supports cash-flow planning, tax provisioning, funding decisions and investment analysis. Automation creates value when it improves those decisions, not merely when it processes more entries.
Plan for incidents before they happen
We recommend evaluating incident response as carefully as prevention. No firm can credibly promise that a cyber incident will never occur. The more useful question is how it will contain the event, preserve evidence and communicate with affected clients.
A response plan should identify decision-makers, escalation contacts and arrangements for suspending compromised access. We also recommend checking how backups are tested and how the business would continue operating if its primary systems became unavailable.
We expect tax providers to distinguish operational disruption from a possible privacy breach. For entities covered by the Privacy Act, the OAIC's Notifiable Data Breaches scheme sets notification obligations for eligible breaches. Not every incident is notifiable, but the assessment should not be postponed or treated as a routine IT task.
If credentials or identity information are exposed, we recommend coordinating the appropriate response with affected organisations and authorities. A compromised account can threaten both confidentiality and the integrity of tax reporting, particularly if bank details or lodged information have been altered.
Ask for evidence before engaging an adviser
We recommend turning security assurances into specific questions during the selection process. Written answers reveal more than broad claims about technology or service quality.
- Registration and scope: We ask which registered practitioner is responsible and which entities and obligations the engagement covers.
- Information handling: We ask how documents are exchanged, who can access them and whether external processors are involved.
- AI governance: We ask which tasks are automated, how confidential data is protected and who reviews material decisions.
- Tax substantiation: We ask how reconciliations, technical conclusions and lodgement approvals are retained.
- Incident response: We ask how clients are contacted, how access is contained and how affected records are checked.
We also assess the exit process. If an engagement ends, we need an orderly transfer of records, clarification of outstanding work and removal of unnecessary access. Tax providers should explain how statutory retention duties affect deletion requests, rather than promising immediate destruction of every record.
For complex groups, we recommend reviewing these controls alongside the broader responsibilities described in our guide to managing complex ATO obligations. Security responsibilities and compliance responsibilities should not sit in separate conversations.
Frequently asked questions
Does using a registered tax agent guarantee protection from an ATO audit? No. We regard registration as an essential credential, not a guarantee against review. Accurate disclosure, sound technical treatment and supporting evidence strengthen a position, but the ATO can still examine it.
Can AI prepare tax information safely? We support controlled AI-assisted processing where confidentiality, access and review requirements are addressed. We do not treat an AI-generated calculation or explanation as sufficient evidence for a tax position without checking the underlying records and applicable law.
What should we expect from tax providers if records are incomplete? We expect missing information to be identified and material limitations explained. We recommend resolving gaps before lodgement wherever possible, rather than replacing evidence with assumptions. Professional advice may be needed on deadlines, amendments and the appropriate reporting approach.
Should our adviser have our myGov password? We recommend keeping personal credentials private. Adviser authority should be established through the appropriate ATO processes, with access limited to what the engagement requires.
Next steps: review security and tax defensibility together
We recommend starting with one entity and tracing a significant transaction from the original document through the ledger, review process and final lodgement. This practical test can reveal missing evidence, unclear approval responsibilities or unnecessary access.
At Perfect Accounting & Tax Services, we bring 25 years of professional experience to accounting, tax and strategic advisory. We support clients across Australia through integrated service capabilities in Adelaide, Sydney and Melbourne, combining financial expertise with AI-driven automation to streamline workflows.
Contact our team for a consultation to discuss your information-handling risks, ATO position and automated accounting workflows. We can help connect compliance requirements with stronger financial visibility and a more informed growth strategy.